ISO 27001 in practice with eAuditor
Manage information security and prepare for an audit
Control IT assets, permissions, and configurations. Prepare reports supporting information security audits in line with ISO 27001.
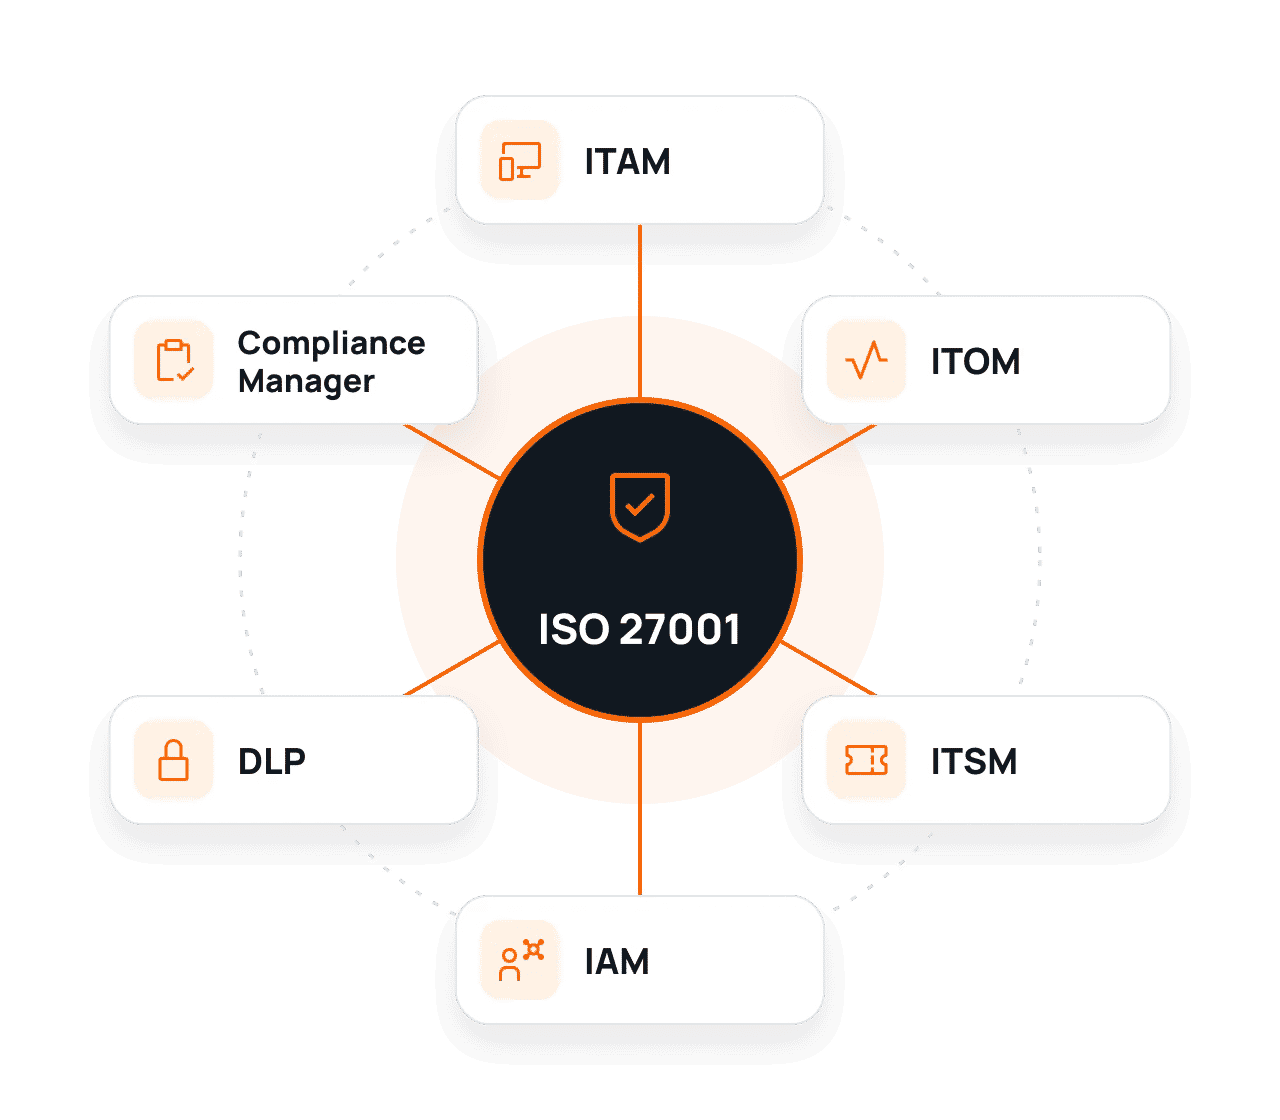
How does eAuditor support ISO 27001 requirements?
Detect irregularities, organize the work of your IT team, and gather information that helps demonstrate the application of selected controls. See how to use these features in the context of ISO 27001.
01
Identify IT Assets
Create an up-to-date inventory of devices and software.
02
Check security controls
Monitor permissions, configurations, and service operation.
03
Prepare data for an audit
Collect reports and a history of actions performed.
eAuditor features supporting ISO 27001
See how individual modules help monitor the IT environment, control access, and prepare reports.
01
ITAM – Full Control Over IT Assets
Automatically detect devices and software. Check their configurations, versions, and change history.
Device and software registry, system versions, and change history.
02
ITOM – IT Infrastructure Monitoring
Track system and service availability. Receive alerts about failures and irregularities.
Service availability history, alerts, event times, and reports.
03
ITSM – Efficient Incident Handling
Log incidents, assign responsible persons, and track corrective actions.
WHAT CAN YOU DOCUMENT?
Tickets, response times, and service history.
04
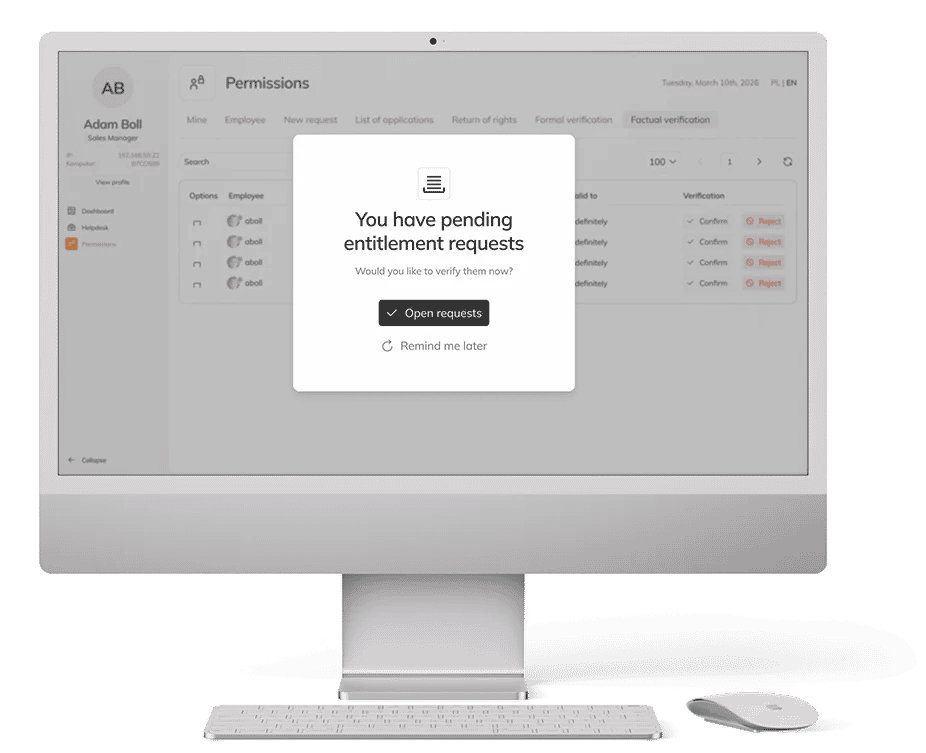
IAM – Access Management
Organize user permissions and review access to systems and resources.
WHAT CAN YOU DOCUMENT?
A list of permissions, access requests, and decisions.
05
DLP – Corporate Data Protection
Control USB media usage and restrict unauthorized data copying.
WHAT CAN YOU DOCUMENT?
Protection policies, incidents, and media usage history.
06
Compliance Manager – Compliance Control
Compare device settings with adopted security policies and detect deviations.
WHAT CAN YOU DOCUMENT?
Inspection results, non-conformity reports, and change history.
Check security controls. Verify settings. Document results.
Technical inspection results help detect deviations and track how they were handled.
How does eAuditor help meet ISO 27001 requirements?
Explore the areas where eAuditor’s functions assist in daily IT operations and documentation collection.
| Area / Requirement | How does eAuditor help? | What can you document? |
|---|---|---|
| Area 01 Asset Inventory Annex A 5.9 | Automatically identify devices and software. ITAM | Asset register, versions and locations. Information owners and classification require a broader process. |
| Area 02 Access Control Annex A 5.15–5.18 | Review permissions and support the access provisioning process. IAM | Access lists, requests and approvals. Authorization rules are defined by the organization. |
| Area 03 Incident Management Annex A 5.24–5.28 | Record tickets and analyse the incident handling process. ITOM + ITSM | Tickets, timelines and activity history. Procedures, roles and incident assessments are also required. |
| Area 04 Monitoring Annex A 8.15–8.16 | Monitor availability and selected infrastructure events. ITOM | Alerts and monitoring history. Monitoring scope should be based on risk assessment. |
| Area 05 Data Leakage Prevention Annex A 8.12 | Apply removable media controls and selected data protection mechanisms. DLP | DLP policies and recorded events. Data classification and handling policies remain separate requirements. |
| Area 06 Configuration Management Annex A 8.9 | Check device settings against established rules. Compliance Manager | Non-compliance reports and change history. Effectiveness assessment also requires audits and reviews. |
Example 01 | Situation
New Device
ITAM detects the device, and Compliance Manager helps verify its settings against rules.
Example 02 | REACTION
Service Failure
ITOM generates an alert, and ITSM organizes ticket handling and action logging.
eAuditor supports more than just ISO 27001
One system, many applications. See how eAuditor helps manage IT security in the context of other regulations and standards as well.
NIS2
Identify vulnerabilities, assess risks, and prioritize corrective actions. Detect weaknesses in IT infrastructure and reduce the risk of security incidents.
DORA
Increase control over ICT systems, monitor their availability, and streamline incident handling. Document actions supporting technological risk management.
KSC
Monitor IT infrastructure, control configurations, and document incidents. Organize cybersecurity activities and prepare reports for controls.
Frequently asked questions about ISO 27001 and eAuditor
eAuditor helps organize the technical areas of information security management: asset inventory, access management, configuration monitoring, and incident documentation. Data from the system can support ISMS-related activities.
IT asset reports, access summaries, configuration control results, change history, and incident handling documentation may be useful — depending on the audit scope and implemented modules.
ITAM collects information about devices and software, helping track their status and changes. This supports maintaining an up-to-date technology asset inventory.
IAM helps organize user access to systems, conduct permission reviews, and document decisions on granting or changing access rights.
Compliance Manager helps compare device configurations against established rules and identifies discrepancies. Reports make it possible to plan corrections and track progress.
Change logs and audit results help identify which settings were modified and where deviations from established standards were detected.
Yes. Functions can be selected to match the organization’s needs and the areas covered by the information security management system, and reports can be used in periodic reviews.
Want to see eAuditor in action?
Check how selected modules can support processes in your organization.