DORA in Practice with eAuditor
DORA in Practice with eAuditor
Control Digital Resilience and Document Activities
Monitor ICT services, manage incidents, and document activities related to digital resilience. Discover eAuditor’s capabilities in the context of DORA.
From Threat Detection to Action Documentation
Detect irregularities, organize IT team work, and collect information that helps demonstrate the application of selected safeguards. See how to use these functions in the context of DORA.
01
Understand the ICT Environment
Check devices, software, and systems used in the organization.
02
Detect and Respond
Monitor service availability and streamline incident handling.
03
Document the Process
Retain alerts, tickets, and activity history for control purposes.
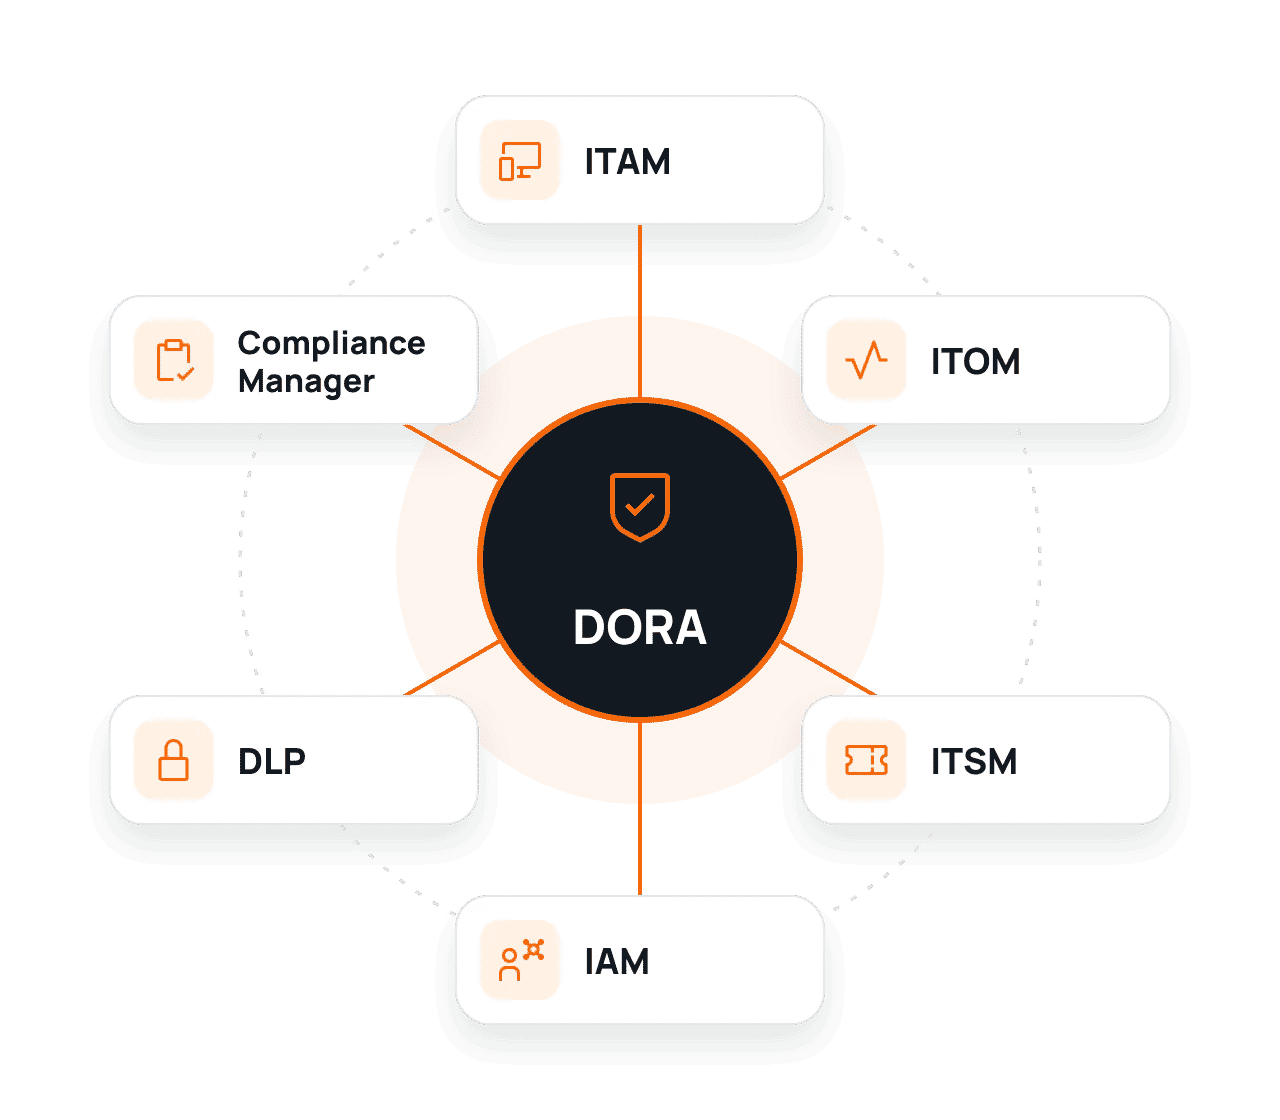
eAuditor Features Supporting DORA
See how individual modules help monitor the IT environment, control access, and prepare reports.
01
ITAM – ICT Asset Management
Gain full insight into devices and software used in the organization. Control configurations, track changes, and maintain an up-to-date inventory of ICT assets.
ICT asset register, software list, and configuration change history.
02
ITOM – ICT System Monitoring
Monitor the availability and operation of ICT systems and services. Receive alerts about failures and irregularities to respond faster to threats.
System availability history, alerts, failure occurrence time, and monitoring reports.
03
ITSM – ICT Incident Management
Register ICT incidents, assign responsible persons, and monitor the progress of corrective actions. Maintain a complete history of ticket handling.
Incident register, response time, ticket history, and corrective actions taken.
04
IAM – ICT System Access Control
Manage user permissions and control access to ICT systems and resources. Streamline reviews and updates of permissions.
List of permissions, history of requests and decisions, and access review results.
05
DLP – Data and Information Protection
Control the use of USB drives and reduce the risk of unauthorized data copying. Implement information protection policies.
Data protection policies, history of media connections, and detected policy violations.
06
Compliance Manager – ICT Security Control
Automatically check device configurations against established security policies. Detect non-compliance and monitor changes.
Configuration compliance reports, detected irregularities, and history of corrective actions.
Detect ICT Problems. Respond Faster. Document Actions.
See how eAuditor supports ICT system monitoring, incident handling, and documentation of activities essential for DORA.
01
Detect Irregularities
Receive alerts about problems with the availability of ICT systems and services.
02
Respond to Incidents
Assign tickets to appropriate individuals and track actions taken.
03
Document Actions
Retain event history and create reports supporting incident analysis.
How Does eAuditor Help Meet DORA Requirements?
Explore the areas where eAuditor’s functions assist in daily IT operations and documentation collection.
| Area / requirement | How does eAuditor help? | What can you document? |
|---|---|---|
| Area 01ICT risk managementArt. 5–16 DORA | Identify ICT assets and check their configurations. Gain better visibility into the state of your infrastructure and the areas that need attention.ITAM + Compliance Manager | Asset register, check results and configuration change history. |
| Area 02Incident detectionArt. 17 DORA | Monitor the operation of your ICT infrastructure, receive alerts about irregularities and improve the logging and handling of events.ITOM + ITSM | Alerts, tickets, event timestamps and response history. |
| Area 03Reporting of major incidentsArt. 18–20 DORA | Collect information about ICT incidents, responsible persons and remedial actions to streamline the preparation of documentation and reports.ITSM + ITOM | Event timeline, ticket history, description of actions taken and technical documentation. |
| Area 04Operational resilienceArt. 11–12, 24–27 DORA | Monitor the availability of critical ICT services, review service interruptions and use technical data when assessing infrastructure resilience.ITOM + ITAM | Availability reports, outage history and lists of monitored assets. |
| Area 05ICT third-party riskArt. 28–30 DORA | See what hardware and software your organization uses. Identify manufacturers, product versions and related ICT assets.ITAM | Lists of devices, software in use, manufacturers and versions. |
| Area 06Access to systemsArt. 9 DORA | Manage user permissions and control the use of removable media. Improve access reviews and the enforcement of information protection rules.IAM + DLP | Permissions list, history of access decisions and events related to removable media control. |
Example 01 | Situation
Critical Service Failure
ITOM detects service unavailability and generates an alert. ITSM allows for ticket assignment and recording of corrective actions.
Example 02 | REACTION
Permission Change
IAM facilitates access control to ICT systems, and DLP helps apply data media usage policies.
eAuditor Supports More Than Just DORA
One system, many applications. See how eAuditor helps manage IT security in the context of other regulations and standards as well.
NIS2
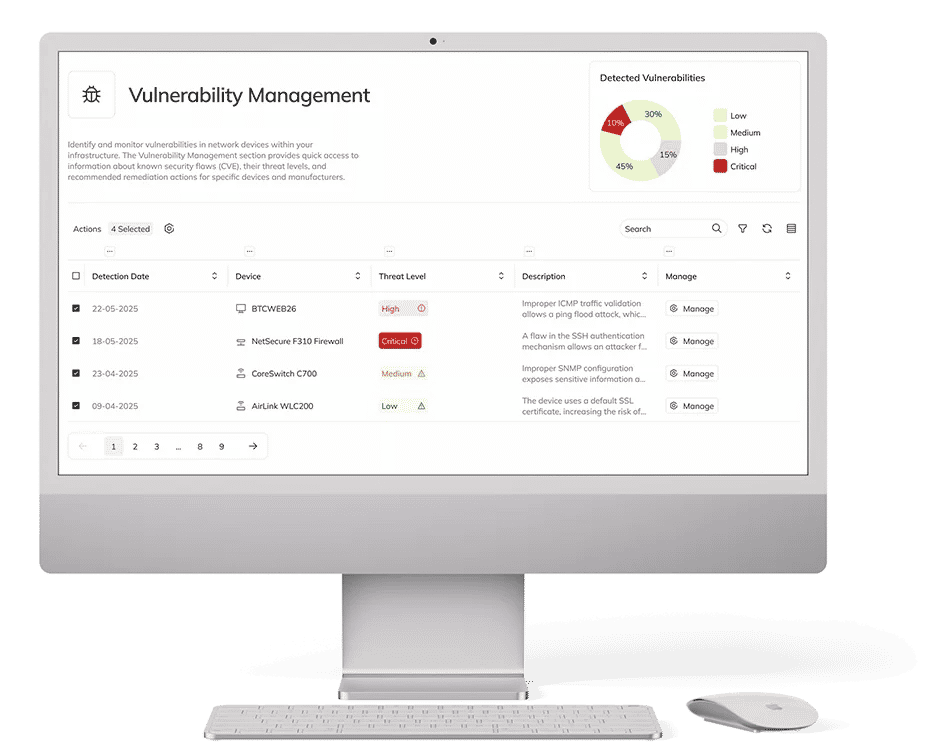
Identify vulnerabilities, assess risks, and prioritize corrective actions. Detect weaknesses in IT infrastructure and reduce the risk of security incidents.
KSC
Monitor IT infrastructure, control configurations, and document incidents. Organize cybersecurity activities and prepare reports for controls.
ISO 27001
Manage IT assets, control permissions, and check device configurations. Collect information needed during security audits.
GDPR
Control data access, manage user permissions, and reduce the risk of unauthorized information copying.
Frequently Asked Questions about DORA and eAuditor
eAuditor helps organize the technical areas of digital operational resilience: ICT asset inventory, service monitoring, incident handling, access control, and reporting. This gives teams easier access to the data they need for DORA-related activities.
ITOM monitors selected services and infrastructure components, logs their availability, and flags irregularities. This lets the team analyze the course of an event faster.
ITSM lets you log tickets, assign responsible staff, and document each stage of handling and remediation. An organized history makes it easier to analyze incidents and prepare data for reporting.
ITAM helps collect information on hardware, software, manufacturers, and versions in use. This provides a valuable starting point for analyzing technological dependencies and conducting ICT vendor reviews.
Yes. The scope of implementation can be tailored to your organization’s priorities, starting for example with inventory and monitoring, then expanding to incident handling and configuration checks.
Reports on assets, availability, configurations, and incident handling provide technical data that supports digital resilience assessments and planning further improvements.
Sources and Verification
- Directive (EU) 2022/2554 (DORA) – text in EUR-Lex ↗
- KNF – DORA incident reporting
- Official description of the eAuditor platform ↗
Disclaimer: eAuditor supports the implementation of selected requirements related to IT management and cybersecurity. The implementation of the platform itself does not mean automatic fulfillment of all legal requirements or certification. The final scope of actions should be determined based on the regulations applicable to a given organization.
Increase Your Organization’s Digital Resilience
Monitor ICT systems, manage incidents, and document activities supporting DORA requirements – all in one system.