IT Configuration Compliance
- Configuration and Software Control
- Data forSecurity Policies
- Support for NIS2, DORA and ISO 27001
Spis treści
Configuration Verification and Compliance Documentation
The eAuditor system provides updated information on devices, operating systems, and applications, which can be used to verify infrastructure compliance with internal security policies. The administrator can analyze configurations, detected software, and inventory reports, then identify areas requiring additional control. Data from ITAM supports the documentation of selected NIS2, DORA, KSC, and ISO 27001 requirements, but does not in itself confirm the organization’s full compliance with these regulations.
Key Capabilities:
- Inventory of Assets Used in the Organization
- System and Configuration Data
- Installed Software Control
- Change History and Reporting
- Evidentiary Material for Compliance Audits
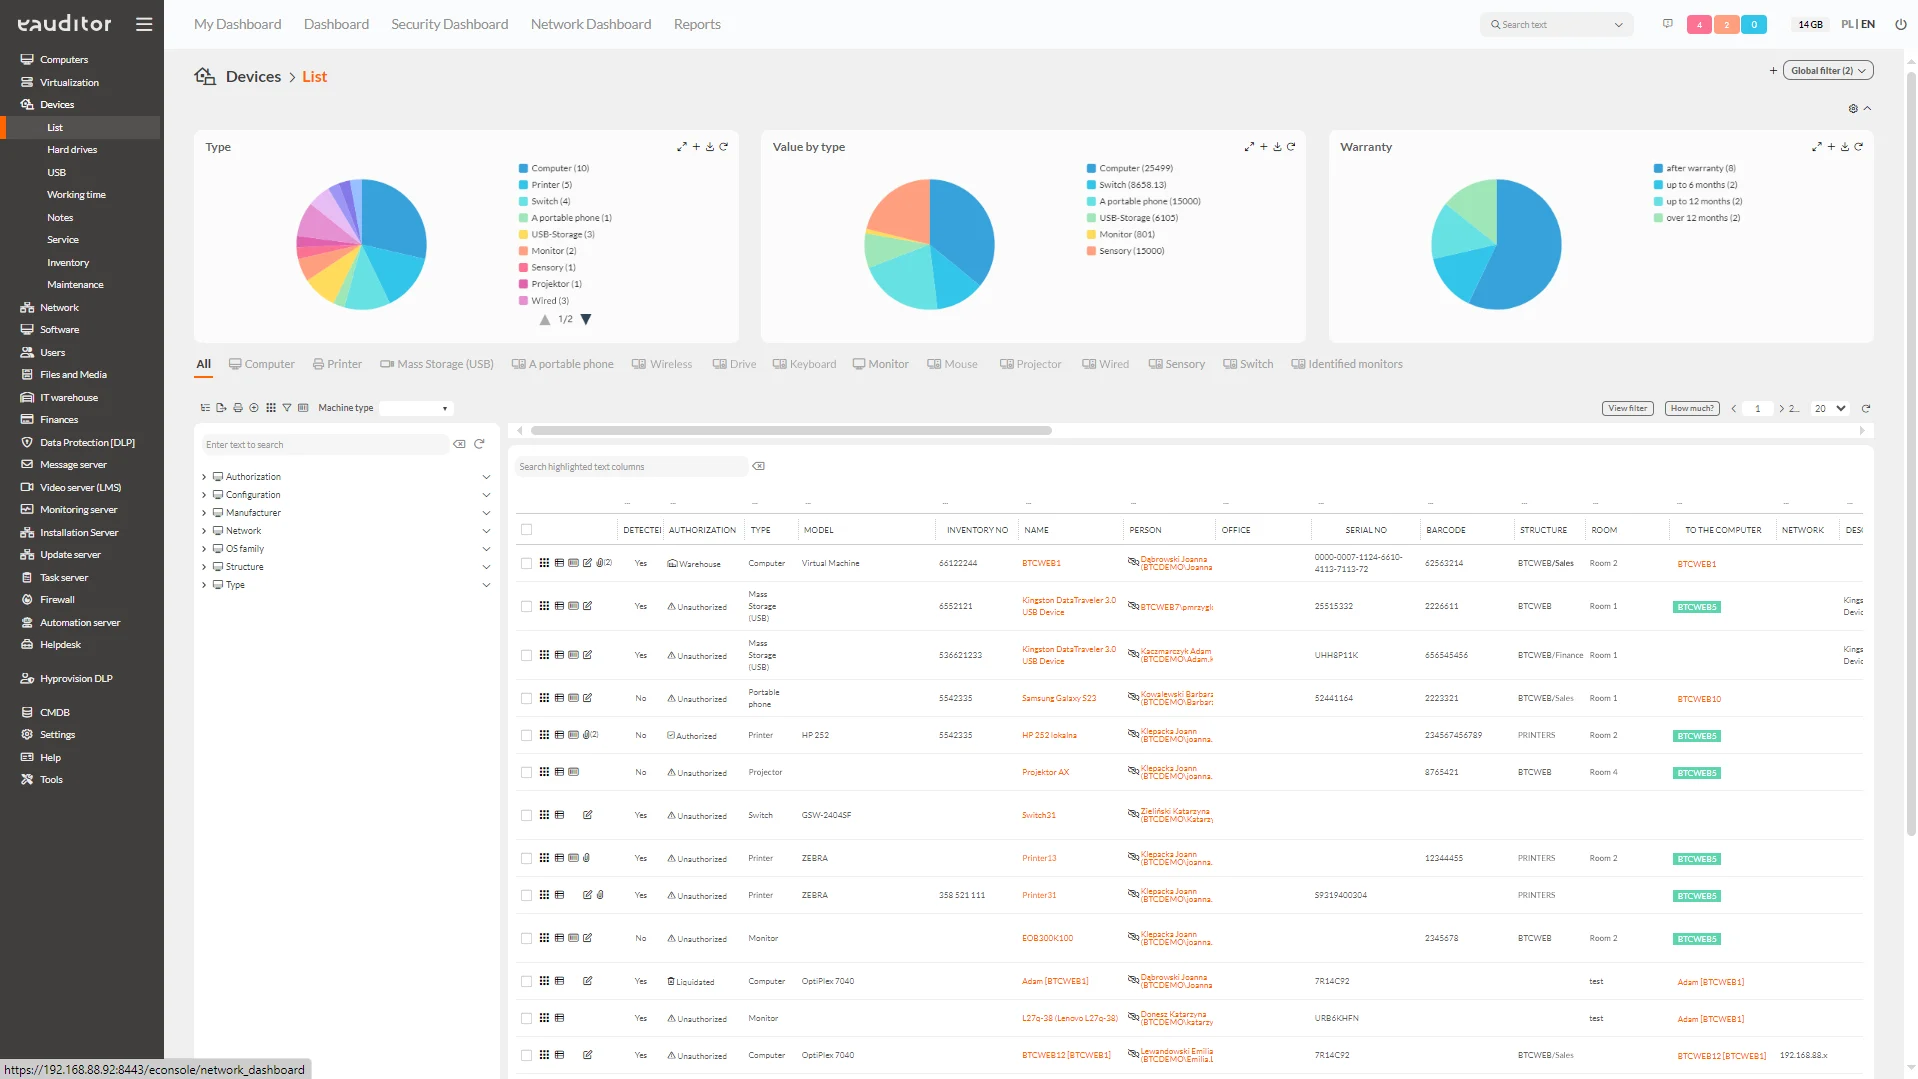
Current Asset List
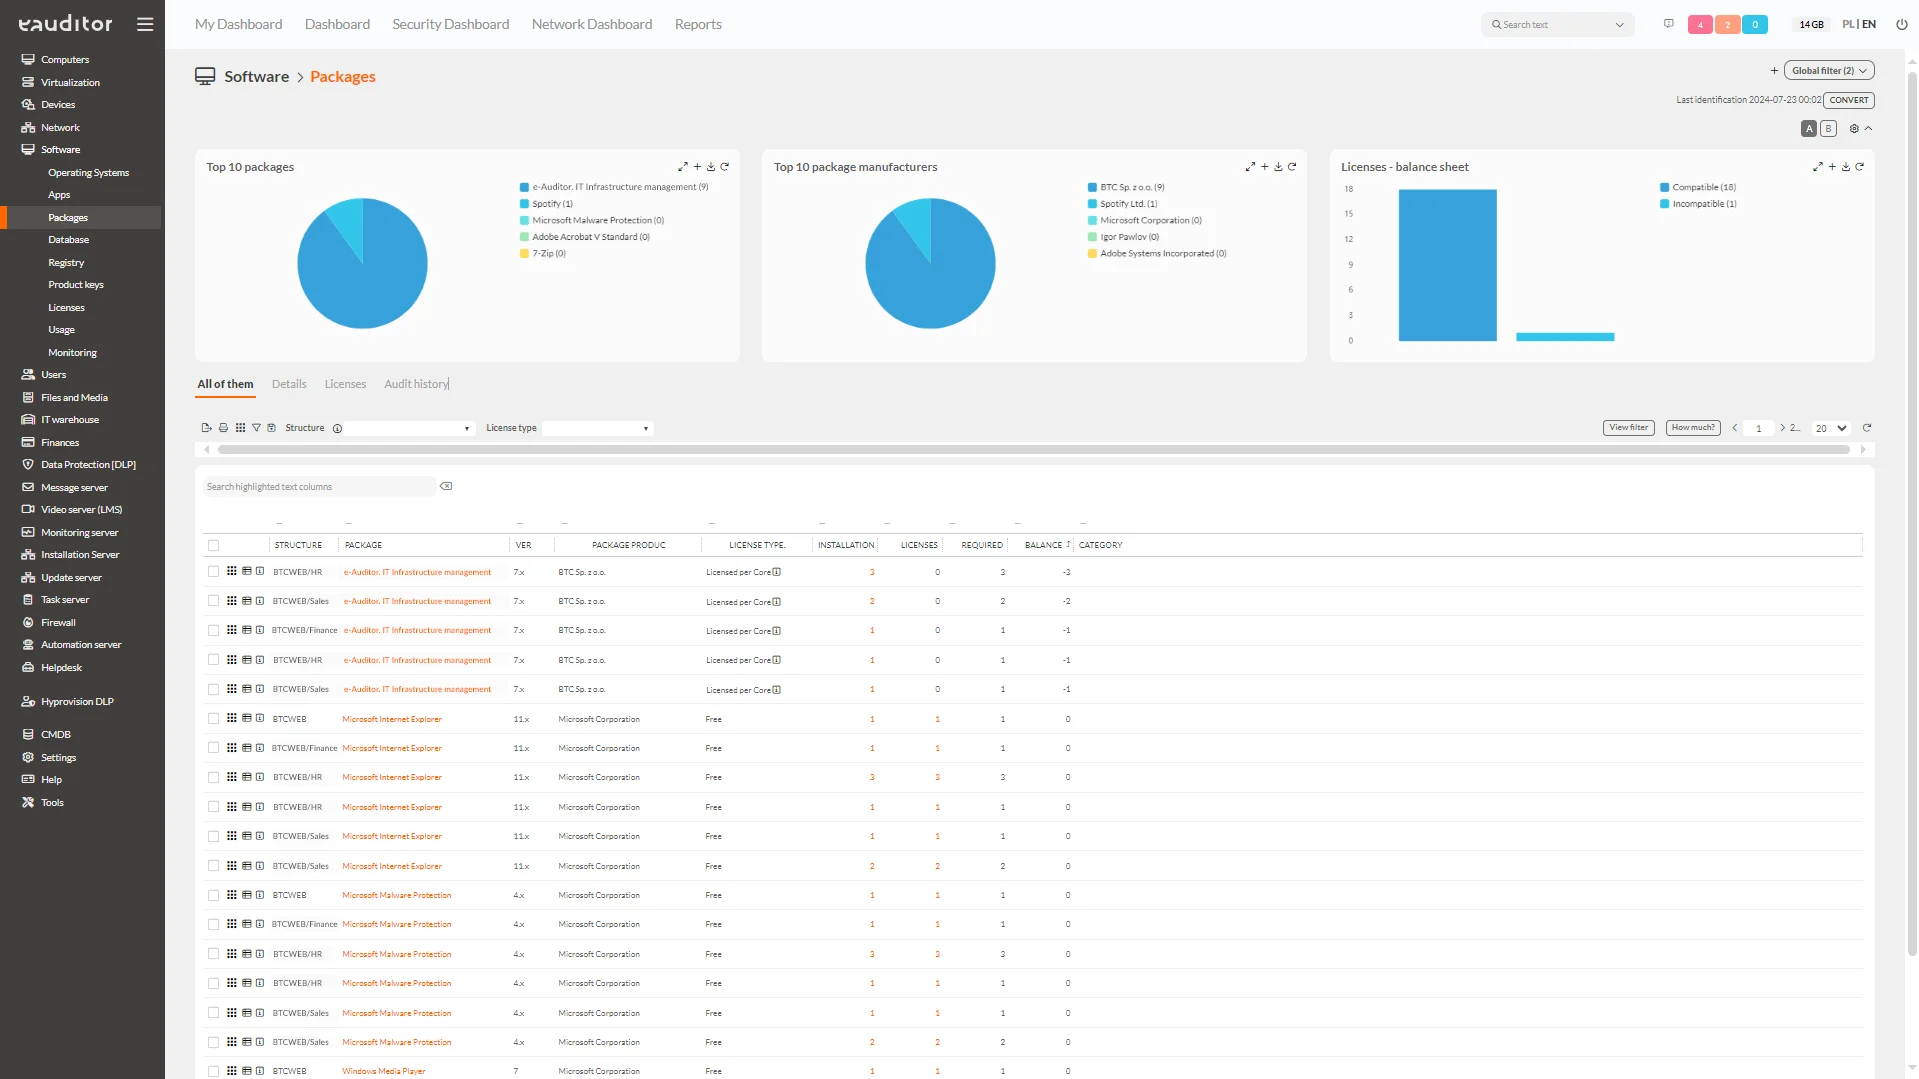
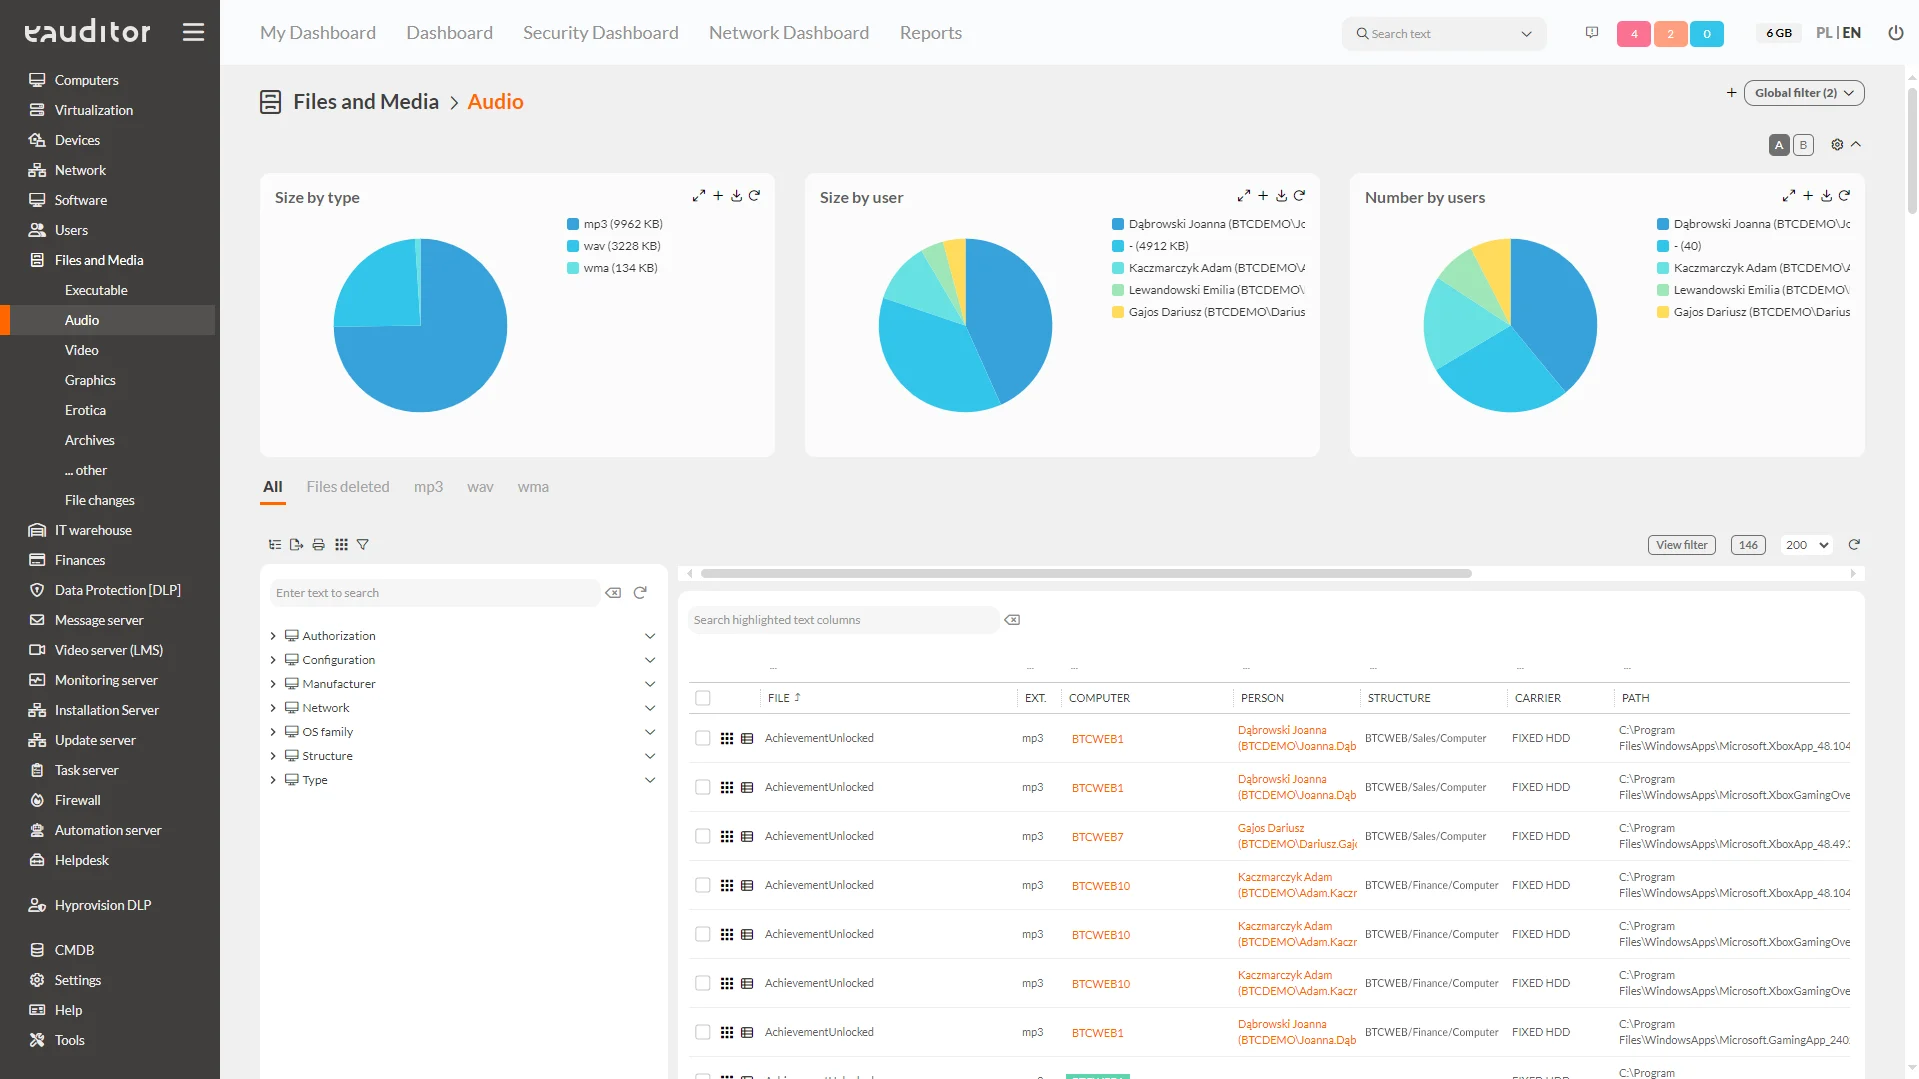
Full control over IT infrastructure requires access to current and detailed information about devices and software used within the organization. eAuditor automatically collects data on computers, servers, operating systems, and installed applications, creating a central register of IT assets.
Administrators can view the technical configuration of devices, identify their users, locations, and analyze the status of individual infrastructure components. Regular updates of inventory data allow for detecting discrepancies between records and the actual state of the IT environment, as well as identifying assets requiring additional control.
The collected information forms the basis for verifying infrastructure compliance with internal security policies and organizational requirements. It also facilitates the preparation of reports, documentation of asset status, and the conduct of internal and external audits.
Configuration and Software
Device configuration and utilized software should comply with technical standards and security principles adopted by the organization. eAuditor allows for analyzing computer and server parameters, operating system versions, and applications installed on individual workstations.
Software classification mechanisms enable marking applications as recommended, prohibited, or requiring additional verification. This allows administrators to identify undesirable installations and devices whose configuration needs checking. The collected information facilitates enforcing internal software policies and maintaining adopted IT environment standards.
Documentation and Audit
During internal and external audits, it is crucial to present reliable information confirming how IT assets are managed. eAuditor provides inventory reports, software summaries, and historical data that can serve as evidentiary material in control processes.
The ability to export summaries facilitates the preparation of documentation for auditors and the presentation of infrastructure verification results. The collected data supports demonstrating compliance with selected requirements of ISO/IEC 27001, NIS2, and DORA regulations, as well as preparing recommendations resulting from the conducted audit.