A single platform for IT management and security
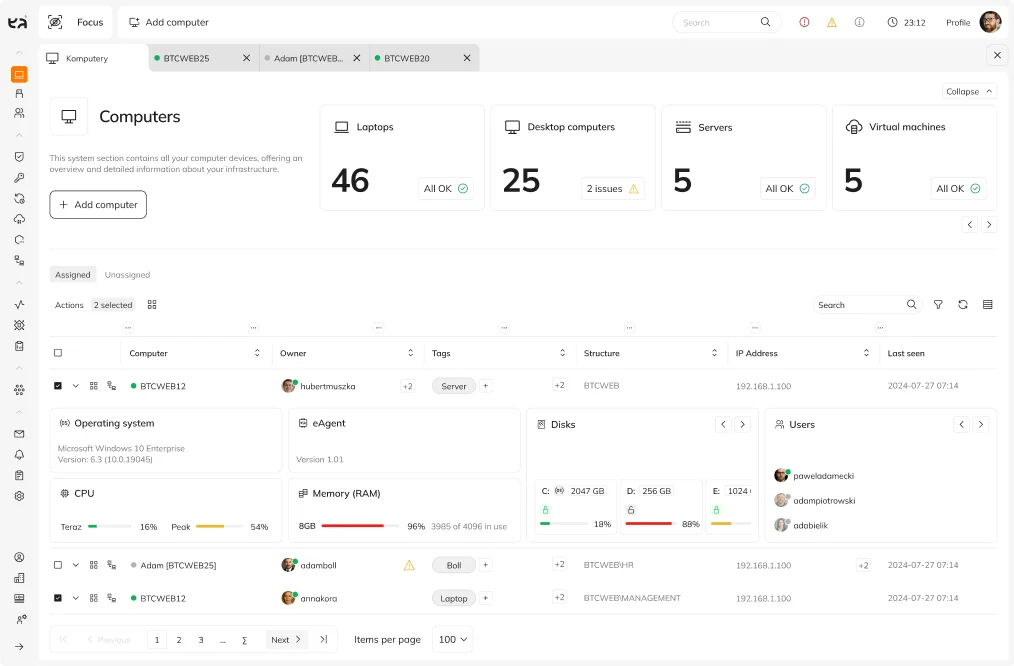
ITAM, ITSM, ITOM, IAM, DLP, and AI in a single system
20+
Years of development
190k+
Monitored devices
1100+
Implementations
3200+
IT Administrators
80+
Partners
NIS2, DORA, ISO 27001, KSC — there are more and more regulations.
Your IT department doesn’t need more tools.
A separate inventory system, a separate help desk, a separate DLP tool, and a separate IAM—that means higher costs, more vulnerabilities, and more work with every audit. eAuditor combines all of this into a single dashboard, ready to demonstrate compliance from day one.

ITAM
IT Resource Management
You know every asset you have—before the auditor asks about it
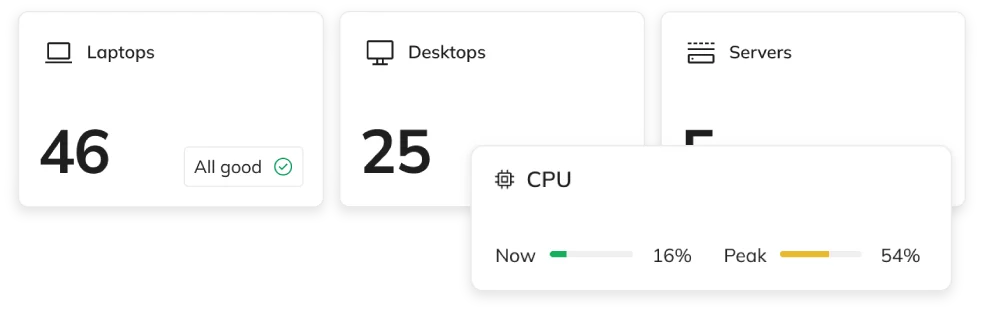
A comprehensive, always up-to-date inventory of the hardware and software required by NIS2 and KSC—no more manual Excel spreadsheets.
Automated hardware and software inventory across the entire network
- History of Configuration Changes and the Device’s Lifecycle
- Electronic Equipment Transfer and Return Reports
- Ready-made audit reports with a single click

ITSM
IT Service Management
Incident reported, handled, and documented—before the statutory deadline expires
NIS2 and KSC require incidents to be reported within 24 and 72 hours. eAuditor provides you with a ready-to-use process and proof that you met the deadline.
- Tickets and incidents in a single dashboard
- A complete history and audit of each case
- Knowledge Base and Employee Self-Service Portal
- A controlled change process, without email chaos

ITOM
IT Operations Management
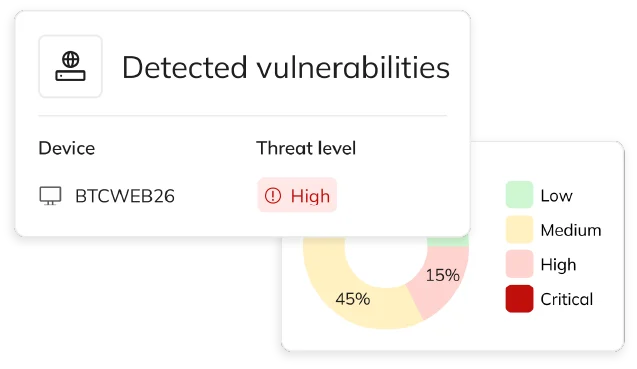
Vulnerability detected before it becomes an incident
Automated patch management and infrastructure monitoring mean less manual work and a lower risk of overlooking something—exactly what NIS2 and ISO 27001 require.
- Real-time Infrastructure Monitoring
- Automated Patch and Vulnerability Management
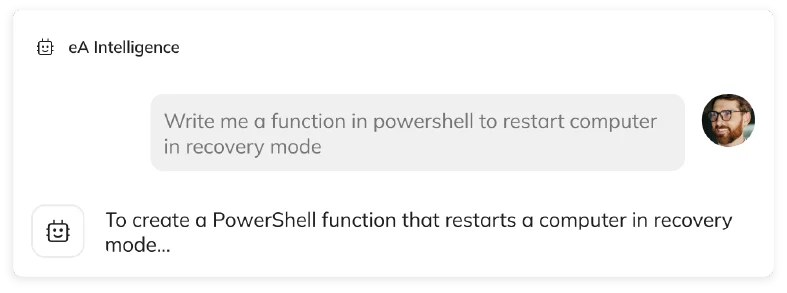
- Remote desktop, remote installation, AI-powered scripts
- Network Maps and Anomaly Alerts

IAM
Identity and Access Management
You know exactly who has access to what and why
Access control is one of the cornerstones of NIS2, DORA, and ISO 27001. eAuditor IAM provides a complete overview of access permissions within an organization—and allows you to correct them immediately.
- Identity, Role, and Permission Management
- MFA and Integration with Active Directory / Entra ID
- Opening Balance Audit — Verification of Assigned Access Rights
- Employee dashboard with a preview of their permissions

DLP
Preventing Data Loss
Your data stays where it’s supposed to be
A data breach is one of the most costly incidents—and one of the most frequently audited by regulators. eAuditor DLP protects data even when offline.
- Checking USB Drives and Ports
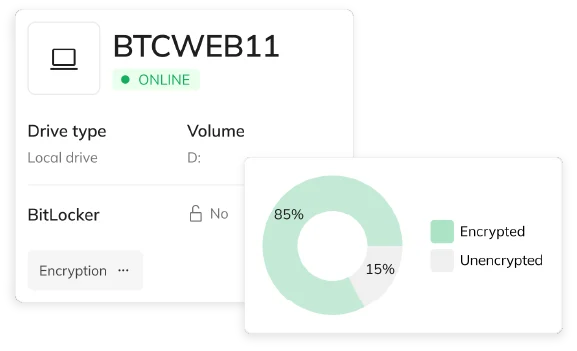
- Full control over BitLocker encryption
- Event logging and detailed security logs
- Locally enforced protection — works even without a network

AI
Artificial intelligence
Automation that ensures compliance for you — 24/7
AI in eAuditor is not an add-on, but rather a layer that supports each of the above areas—reducing human error and enabling a faster response to threats.
- Real-time anomaly detection
- AI-Powered Scripts and Automations
- Smart Support for IT Administrators
- Automatic document anonymization (integration with Bluur)
Compliance: Supports the implementation of NIS2, DORA, ISO 27001, and KSC requirements in all of the above areas
Six areas. Four regulations. One answer.
| Moduł | NIS2 | DORA | ISO 27001 | KSC |
|---|---|---|---|---|
| ITAM | ||||
| ITSM | ||||
| ITOM | ||||
| IAM | ||||
| DLP | ||||
| AI |
We are trusted by more than 900 customers
You’re not buying six tools. You’re buying one.

On-premises or in the cloud
You choose the model

Deployment of even the largest environments
up to 15,000 computers in a single installation

Protection Even When Offline
The local agent enforces policies without a network connection

20+ years of growth
experience with the Polish regulatory environment
FAQs
Yes. eAuditor combines, among other things, ITAM, ITSM, ITOM, IAM, and DLP into a single platform, reducing the need to use multiple independent systems.
No. Individual areas can be implemented in phases, in accordance with the organization’s needs and priorities.
Yes. eAuditor cloud® operates on a SaaS model. An eAuditor On-Premise version, installed on the customer’s infrastructure, is also available.
eAuditor supports organizations in implementing, documenting, and monitoring selected requirements under NIS2, DORA, ISO 27001, and KSC. The scope of support depends on the implemented features and the specific nature of the organization.
Yes. The system can support devices located outside the local network, including those behind NAT, and the agent can enforce selected policies locally without a constant connection to the server.
Yes—eAuditor offers full integration with Active Directory and Microsoft Entra ID, enabling automatic synchronization of user accounts and organizational structures, as well as efficient identity and access management (IAM).
Yes. Free trials and demonstrations of the solution are available, depending on the model selected and the scope of implementation. Check it out.
Yes. eAuditor is used in environments with thousands of devices; a single installation can support up to 15,000 computers. There are no limits on the number of computers for the eAuditor cloud version.
Yes. Certain security mechanisms, including the enforcement of DLP policies, can operate locally on the device even without a network connection.
The price depends on the deployment model you choose and the number of devices:
-
eAuditor Cloud: Billed through a flexible subscription (SaaS) with monthly or annual payments—see the eAuditor Cloud price list for details.
-
eAuditor On-Premise: A license for your own server, priced individually based on your organization’s needs.